
Medical Device Security Market Report Scope & Overview:
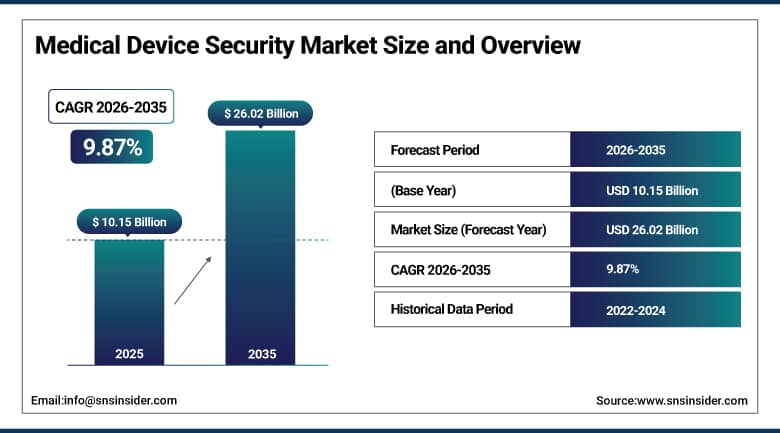
The Medical Device Security Market was valued at USD 10.15 Billion in 2025 and is projected to reach USD 11.15 Billion in 2026 and USD 26.02 Billion by 2035, registering a CAGR of 9.87% over the forecast period. Growth is anchored in the rapid connection of infusion pumps, imaging systems, monitors, and implants to hospital networks, together with stricter premarket cybersecurity rules and a steady rise in attacks on healthcare organizations. Hospitals and manufacturers are buying asset discovery, risk scoring, network segmentation, and software supply chain tools to keep connected devices safe without interrupting patient care.
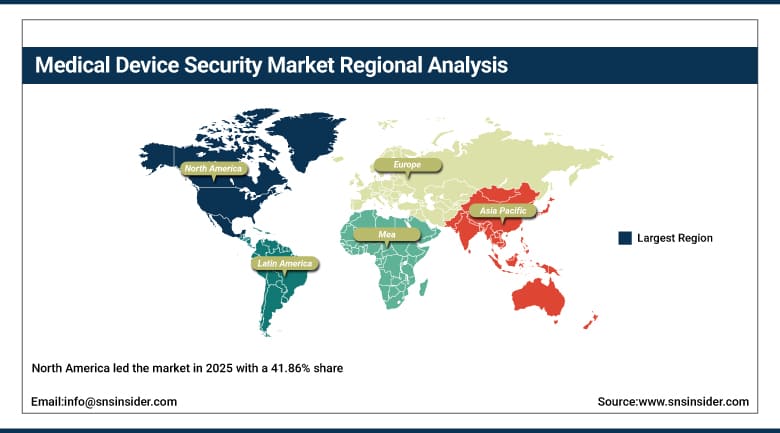
North America accounted for the largest share of the market at 41.86% in 2025, supported by binding premarket requirements for cyber devices, a large installed base of connected equipment, and a concentrated group of specialist vendors. The United States leads regional demand because health systems face constant ransomware pressure and must document device risk for regulators and insurers. Asia Pacific is the fastest growing region, helped by hospital digitization, expanding connected equipment fleets, and rising cybersecurity spending across China, Japan, India, South Korea, and Australia. Managed monitoring and cloud-based visibility are the main purchasing priorities in both regions.
To Get More Information On Medical Device Security Market - Request Free Sample Report
Key Report Takeaways
-
By component, solutions held a 66.84% share in 2025, while services are the fastest growing.
-
By device type, hospital medical devices accounted for 46.31% of the market in 2025, while wearable and external medical devices are the fastest growing.
-
By deployment mode, on-premises deployments led with a 57.46% share in 2025, while cloud-based deployments are the fastest growing.
-
By end user, healthcare providers represented 44.31% of the market in 2025, while medical device manufacturers are the fastest growing.
-
By region, North America led with a 41.86% share in 2025, while Asia Pacific is expected to expand fastest at a CAGR of 10.89%.
Market Trends and Insights
Security is moving into the device design stage. Manufacturers now generate software bills of materials, run threat modeling, and plan vulnerability disclosure before submission, so protection is built in rather than added after launch.
Asset visibility is becoming a platform function. Vendors that began with passive network discovery are adding risk scoring, vulnerability prioritization, and automated segmentation, which gives hospitals one view across clinical, operational, and information technology assets.
Consolidation is reshaping supply. Large technology and security groups are acquiring specialist healthcare security firms, and buyers increasingly prefer suppliers that connect device security with broader exposure management.
Legacy equipment remains the central problem. Devices that cannot be patched stay in service for many years, so compensating controls such as segmentation, virtual patching, and behavior monitoring are in strong demand.
Drivers Impact Analysis
|
Driver |
(~) Percentage Point Impact on Market CAGR |
Geographic Relevance |
Impact Timeline |
|---|---|---|---|
|
Rising cyberattacks and ransomware targeting healthcare organizations |
+2.48% |
Global |
Short term (2 years or less) |
|
Stricter premarket and postmarket cybersecurity regulation |
+2.12% |
North America, Europe |
Short term (2 years or less) |
|
Growth of connected, wearable, and remote monitoring devices |
+1.86% |
Global |
Medium term (2 to 4 years) |
|
Hospital digitization and cloud adoption |
+1.34% |
Asia Pacific, Europe |
Medium term (2 to 4 years) |
|
Demand for software bills of materials and supply chain assurance |
+0.95% |
North America, Europe |
Long term (4 years or more) |
Rising Cyberattacks and Ransomware Targeting Healthcare Organizations
Healthcare organizations hold valuable data and cannot tolerate long outages, which makes them a favored target for ransomware groups. Medical devices add risk because many run older operating systems, use default credentials, and cannot be scanned like ordinary computers. An attack that reaches clinical networks can force diversion of ambulances, cancellation of procedures, and a return to paper records. Boards and insurers now treat device security as a patient safety issue, and they approve budgets for visibility, segmentation, and incident response tools that protect clinical operations.
Stricter Premarket and Postmarket Cybersecurity Regulation
Regulators have turned expectations into requirements. For instance, in February 2026, the U.S. Quality Management System Regulation took effect, and its new compliance program explicitly covers cyber devices under Section 524B of the Federal Food, Drug, and Cosmetic Act. Manufacturers must show secure design, vulnerability monitoring, and patch processes, while hospitals are asked to assess device risk against published guidance. These rules create demand for testing, software bill of materials management, and monitoring tools on both the manufacturer and provider sides.
Growth of Connected, Wearable, and Remote Monitoring Devices
Connected insulin pumps, cardiac monitors, wearables, and home medical equipment send data to cloud services and mobile applications, which widens the attack surface well beyond the hospital walls. Remote patient monitoring programs rely on devices that patients install themselves on home networks, with limited control by providers. Manufacturers must therefore secure device firmware, mobile applications, and cloud back ends together. This expansion increases demand for application security, identity management, and continuous monitoring services that follow devices across settings and throughout their long operational lives.
Hospital Digitization and Cloud Adoption
Hospitals are replacing paper processes with electronic records, imaging archives, and cloud analytics, and each project connects more equipment to shared networks. Newly built facilities often specify thousands of connected devices from the outset, and security teams need tools that can discover and classify them automatically. Cloud-based security platforms allow smaller hospitals to obtain monitoring without hiring specialist staff. As digital programs spread across Asia Pacific and Europe, the number of hospitals that need device security grows, and vendors can expand beyond large academic centers.
Demand for Software Bills of Materials and Supply Chain Assurance
A software bill of materials lists every component inside a device, which allows hospitals and manufacturers to find affected products quickly when a new vulnerability is published. Regulators now expect manufacturers to provide this information, and buyers ask for it during procurement. Managing these inventories across product lines requires specialized tools that match components with vulnerability databases and track remediation. Because devices stay in service for a decade or longer, supply chain assurance creates recurring demand for monitoring and update services over the full product lifecycle.
Restraints Impact Analysis
|
Restraint |
(~) Percentage Point Impact on Market CAGR |
Geographic Relevance |
Impact Timeline |
|---|---|---|---|
|
Legacy devices that cannot be patched or replaced |
-1.58% |
Global |
Long term (4 years or more) |
|
Shortage of skilled cybersecurity and clinical engineering staff |
-1.14% |
Global |
Medium term (2 to 4 years) |
|
Operational risk of scanning and blocking clinical devices |
-0.82% |
North America, Europe |
Short term (2 years or less) |
|
Budget constraints and fragmented responsibility in hospitals |
-0.64% |
Latin America, Middle East & Africa, Asia Pacific |
Medium term (2 to 4 years) |
Legacy Devices That Cannot Be Patched or Replaced
Many imaging systems, monitors, and laboratory instruments remain in service for ten years or more, and their manufacturers may no longer supply security updates. Replacing them is expensive, and clinical teams resist taking devices offline for upgrades. Security vendors can isolate such equipment, but segmentation projects are complex and slow. Hospitals therefore carry large amounts of residual risk, and some purchasing decisions are delayed while leaders decide whether to spend on protection, replacement, or a combination of both approaches across their equipment fleets.
Shortage of Skilled Cybersecurity and Clinical Engineering Staff
Medical device security requires people who understand both clinical workflows and network defense, and such professionals are scarce. Hospital security teams are often small, and clinical engineering departments may lack training in cybersecurity. Without staff to review alerts and act on findings, tools can sit underused. Smaller hospitals in particular cannot afford dedicated analysts. This gap slows deployment, raises demand for managed services, and limits how quickly buyers can convert purchased technology into measurable reductions in risk across their clinical environments.
Operational Risk of Scanning and Blocking Clinical Devices
Active scanning or automatic blocking can interrupt a device that is delivering therapy, so clinical leaders insist on passive methods and careful change control. Policies that block traffic may also disrupt vendor support connections or data feeds that clinicians depend on. These concerns lengthen proof-of-concept periods and limit how much automation hospitals will allow. Vendors must demonstrate safe operation across many device models, which adds testing cost and slows the introduction of features that would otherwise close security gaps more quickly.
Budget Constraints and Fragmented Responsibility in Hospitals
Responsibility for device security is often split among information technology, clinical engineering, and device manufacturers, and no single budget covers the full lifecycle. Hospitals in developing regions face tighter funding and prioritize clinical equipment over security software. Payment for cybersecurity is rarely reimbursed, so spending must compete with other needs. Unclear ownership leads to delays in policy decisions and procurement, and many organizations buy only after an incident or an audit finding exposes the gap in protection across the facility.
Medical Device Security Market Segment Analysis
By Component, Solutions Dominate Medical Device Security Market; Services to Register Fastest Growth.
Solutions held a 66.84% share in 2025 because hospitals and manufacturers first purchase the platforms that discover assets, assess vulnerabilities, monitor network behavior, and enforce segmentation. These products include encryption, endpoint protection, network security, and application security tools that are licensed per device or per facility. Technology buyers favor software they can deploy quickly, and the breadth of product categories gives vendors many opportunities to sell additional modules to existing customers over time as their security programs mature and expand.
Services are expected to expand at a CAGR of 11.46% from 2026 to 2035, driven by the shortage of internal security staff and the complexity of device environments. Hospitals use consulting for risk assessments, integration partners for segmentation projects, and managed providers for continuous monitoring and incident response. Manufacturers buy penetration testing and software bill of materials services to prepare regulatory submissions. As buyers look for results rather than tools, service contracts grow faster than license revenue in most regions.
By Device Type, Hospital Medical Devices Dominate Medical Device Security Market; Wearable and External Medical Devices to Register Fastest Growth.
Hospital medical devices accounted for 46.31% of the market in 2025 because infusion pumps, patient monitors, imaging systems, and ventilators form the largest connected fleets in care facilities. These devices are networked, handle sensitive data, and directly affect patient safety, so they receive the first security investment. Many run older software and remain in service for years, which makes network-based controls essential. Large health systems also have inventories that justify enterprise security purchases and dedicated project budgets for each year.
Wearable and external medical devices are projected to grow at a CAGR of 12.38% between 2026 and 2035, as continuous glucose monitors, insulin pumps, cardiac patches, and home equipment connect to phones and cloud platforms. These products operate outside hospital networks, so manufacturers must embed protection into firmware, applications, and back-end services. Regulators examine the cybersecurity of such devices closely, and patients expect their health data to be protected, which drives spending on testing, encryption, and monitoring across product lifecycles.
By Deployment Mode, On-Premises Dominates Medical Device Security Market; Cloud-Based to Register Fastest Growth.
On-premises deployments held a 57.46% share in 2025 because hospitals prefer to keep sensor appliances, analysis engines, and data inside their own networks. Clinical environments involve sensitive information and strict uptime requirements, so security teams value direct control. Passive monitoring appliances placed on network switches are a common design for device discovery, and many existing contracts are renewed rather than replaced. Public and defense-related healthcare institutions also face policies that discourage external hosting of device data in outside facilities.
Cloud-based deployments are projected to grow at a CAGR of 12.07% between 2026 and 2035 as vendors offer subscription pricing, faster updates, and shared threat intelligence from thousands of facilities. Smaller hospitals can obtain monitoring without maintaining analysis servers, and large systems value consistent management across many sites. Improved security certifications and regional hosting options are reducing earlier objections, and hybrid designs that keep sensors local while analytics run in the cloud are becoming a common compromise for large groups.
By End User, Healthcare Providers Dominate Medical Device Security Market; Medical Device Manufacturers to Register Fastest Growth.
Healthcare providers represented 44.31% of the market in 2025 because hospitals and health systems operate the connected devices, hold the patient data, and bear the operational impact of an attack. Their security teams buy discovery, segmentation, and monitoring tools to meet accreditation, insurance, and regulatory expectations. Large systems with many sites invest in enterprise platforms, and consolidation of hospital networks increases the scale of purchases. Providers remain the largest customer group for both software and services in every region.
Medical device manufacturers are expected to expand at a CAGR of 11.58% from 2026 to 2035, since premarket cybersecurity requirements now apply to new and updated products. Manufacturers invest in threat modeling, secure development tools, software bill of materials management, penetration testing, and vulnerability response programs. Postmarket monitoring of products already in the field adds a continuing need. Companies that fail to demonstrate sound practices risk delays in regulatory clearance, which makes security a core part of product development budgets.
Geography Analysis
|
Region |
Major Country |
Share within Region, 2025 (%) |
|---|---|---|
|
North America |
United States |
90.12% |
|
Europe |
Germany |
25.93% |
|
Asia Pacific |
China |
30.48% |
|
Middle East & Africa |
Saudi Arabia |
29.58% |
|
Latin America |
Brazil |
42.77% |
North America Medical Device Security Market
North America led the market in 2025 with a 41.86% share, supported by binding premarket requirements for cyber devices, a large installed base of connected equipment, and a concentrated group of specialist security vendors. The United States contributes most of the regional demand, with its 2025 value estimated at USD 3.83 Billion and a projected CAGR of 10.12% through 2035. Health systems face constant ransomware pressure, and they must document device risk for regulators, insurers, and accreditation bodies, and spending is shifting from pilot projects to enterprise programs.
Regulatory and industry actions continue to shape purchasing. For example, in January 2026, the U.S. Food and Drug Administration issued a warning letter to Beta Bionics, widely described as the first publicly visible letter to cite a cybersecurity failure explicitly. Hospitals responded by tightening supplier requirements, and several state agencies issued guidance asking hospitals to assess device security. Canada adds demand through provincial health system programs and growing attention to critical infrastructure protection, which is encouraging hospitals to formalize their device inventories and response plans.
Get Customized Report as Per Your Business Requirement - Enquiry Now
Europe Medical Device Security Market
Europe held the second-largest share of the market, with Germany leading country demand through its large hospital sector, strong medical device industry, and national cybersecurity requirements for critical facilities. The United Kingdom, France, and the Nordic countries also invest steadily, often through national health system programs for cyber resilience. Buyers favor suppliers that provide local hosting, multilingual support, and compliance with European data protection law, which gives regional specialists a place alongside multinational security groups bidding for the same hospital contracts.
Regulation shapes demand on several fronts. Manufacturers must satisfy the medical device regulation, which requires cybersecurity risk management, and hospitals fall under network and information security rules that raise obligations for essential service operators. A new cyber resilience law for digital products adds further duties for manufacturers. These overlapping requirements push both sides toward documented security programs, and they favor vendors that can map product features to European compliance frameworks and reporting templates used by regulators and external independent auditors.
Asia Pacific Medical Device Security Market
Asia Pacific is the fastest growing region, with a projected CAGR of 10.89% from 2026 to 2035. China holds the largest national share, driven by hospital digitization, large connected equipment fleets, and national requirements for data and network security. Japan and South Korea contribute through advanced hospital networks and strong device manufacturing, while India and Australia expand demand through new digital health programs. Rising health spending and growing awareness of ransomware widen the number of hospitals that can invest in protection.
Many regional hospitals are connecting equipment at scale for the first time, which lets them include security in the initial design. Local security vendors are adapting products to national standards and languages, and global suppliers are signing distribution and managed service agreements with regional partners. Manufacturers in the region that export devices to the United States and Europe must meet foreign premarket cybersecurity rules, which spreads secure development practices and raises demand for testing and assurance services across Asian economies.
Latin America Medical Device Security Market
Latin America accounted for 5.62% of the market in 2025, with Brazil representing the leading national market. Large private hospital groups and diagnostic chains in Brazil and Mexico are investing in network monitoring and segmentation after repeated attacks on health organizations in the region. Public hospitals adopt more slowly because of budget limits and thin security teams. International vendors work through local integrators, and currency volatility can delay purchases of tools priced in dollars, so subscription billing in local currency is increasingly favored.
Managed security services are a practical entry point because hospitals can obtain monitoring without hiring specialized staff. Data protection laws in Brazil, Mexico, and Argentina are increasing the responsibility of providers for patient information, which supports investment in security controls. Insurance providers are also asking for evidence of basic protections before issuing cyber coverage, a requirement that is gradually reaching hospitals and encouraging them to inventory and protect connected clinical equipment and prepare formal incident response plans for every unit.
Middle East & Africa Medical Device Security Market
The Middle East and Africa represented the smallest share at 5.41% in 2025. Saudi Arabia leads the regional market, supported by national health transformation programs, new hospital projects, and government cybersecurity mandates for critical sectors. The United Arab Emirates and Qatar follow with early adoption in flagship hospitals and healthcare cities. Gulf governments prefer integrated packages from established suppliers, which creates opportunities for vendors that provide training, local support, and managed monitoring on long-term contracts across several hospitals and clinics.
South Africa provides most of the demand in Africa, where private hospital groups invest in network protection and incident response. Elsewhere on the continent, adoption is constrained by funding, limited connectivity, and a shortage of trained cybersecurity staff. Donor-supported digital health programs and public-private partnerships are therefore important routes to market. Simple, managed services that do not require large in-house teams are better suited to these conditions than complex enterprise platforms that demand specialist skills and large in-house teams of analysts.
Competitive Landscape
The Medical Device Security Market shows a fragmented structure. Network security leaders, industrial and connected device specialists, healthcare-focused start-ups, and medical device makers all compete for hospital and manufacturer budgets. Large technology and cybersecurity groups hold broad portfolios and global reach, while specialists win projects through deep knowledge of clinical device protocols and workflows. Buyers increasingly prefer suppliers that connect device security with wider exposure management, and this preference is encouraging acquisitions and platform partnerships.
Vendors follow four main strategic lines. Acquisitions bring healthcare security specialists into larger platforms, partnerships connect device visibility with network, identity, and exposure management tools, product launches extend software supply chain and vulnerability prioritization features, and managed services help hospitals that lack internal staff. Companies also invest in clinical safety validation, since hospitals will not enable automated blocking unless vendors can show that protection will not interrupt therapy or monitoring.
Medical Device Security Market Industry Leaders
1. Palo Alto Networks, Inc.: Network security leader offering medical device discovery, segmentation, and zero trust controls for healthcare networks.
2. Cisco Systems, Inc.: Network infrastructure and security supplier whose switching and visibility products underpin many hospital device programs.
3. Check Point Software Technologies Ltd.: Cybersecurity provider with healthcare device protection and a partnership model for medical IoT security.
4. Armis, Inc.: Asset visibility and exposure management company covering connected medical devices across clinical environments.
5. Claroty Ltd.: Specialist in cyber-physical systems protection with a dedicated healthcare device security offering.
Companies Covered in this Report
-
Palo Alto Networks, Inc.
-
Cisco Systems, Inc.
-
Check Point Software Technologies Ltd.
-
Armis, Inc.
-
Claroty Ltd.
-
Forescout Technologies, Inc.
-
Axonius, Inc. (Cynerio)
-
Ordr, Inc.
-
Medcrypt, Inc.
-
Synopsys, Inc.
-
ClearDATA
-
GE HealthCare
-
Fortinet, Inc.
-
Zscaler, Inc.
Recent Industry Developments
-
July 2025: Axonius acquired Cynerio, a medical device security specialist, in a deal reported at more than USD 100.00 million.
-
December 2025: ServiceNow agreed to acquire Armis for USD 7.75 Billion to extend cyber exposure management across information technology, operational technology, and medical devices.
-
January 2026: Beta Bionics received a U.S. warning letter that cited a vulnerability in its insulin pump and a missed correction report, a landmark case for device cybersecurity enforcement.
-
February 2026: The U.S. Quality Management System Regulation took effect, aligning device quality requirements with international standards and covering cyber devices through a new compliance program.
-
May 2026: The initial target for an updated HIPAA Security Rule passed without a revised timeline from federal health regulators, leaving hospitals planning for stricter requirements.
-
2026: The Joint Commission launched a Cyber Resilience Readiness certification for healthcare organizations.
Scope and Research Methodology
This study defines the Medical Device Security Market as the software, hardware, and services used to discover, assess, protect, and monitor connected medical devices and the networks, applications, and cloud services they depend on, for both healthcare providers and device manufacturers. The base year is 2025, the forecast period runs from 2026 to 2035, and all values are expressed in USD. The market is segmented by component, device type, deployment mode, end user, and region, and each segment is reported with its 2025 share and its forecast growth rate. Regional coverage spans North America, Europe, Asia Pacific, Latin America, and the Middle East and Africa, with country-level detail for the leading national markets in each region.
The research program combines secondary and primary work. Secondary research draws on company annual reports, investor presentations, regulatory filings, device authorization records, government and industry advisories, trade association data, product documentation, and peer-reviewed and industry publications. Primary research consists of structured interviews and surveys with executives, product and business heads, security architects, clinical engineers, regulatory affairs managers, and hospital technology leaders across the value chain. These conversations validate assumptions on adoption rates, pricing, deployment models, and compliance practices. Interview findings are compared across respondent groups so that vendor views are tested against buyer experience, and conflicting answers are resolved through follow-up discussions before they are accepted.
Market engineering follows a bottom-up build from vendor revenue, installed base, and adoption data, which is then cross-checked top-down against hospital security spending, connected device counts, and sector indicators. Triangulation across these routes narrows differences before figures are finalized. Forecasts take into account threat trends, regulation, technology cost curves, staffing conditions, and macroeconomic factors in each region. Every estimate passes a structured analyst quality review for consistency across segments and regions before it is released in the report. Estimates are refreshed as new regulatory decisions, company disclosures, and procurement data become available during the research cycle.
Medical Device Security Market Report Scope:
| Report Attributes | Details |
|---|---|
| Market Size in 2025 | USD 10.15 Billion |
| Market Size by 2035 | USD 26.02 Billion |
| CAGR | CAGR of 9.87% From 2026 to 2035 |
| Base Year | 2025 |
| Forecast Period | 2026-2035 |
| Historical Data | 2022-2024 |
| Report Scope & Coverage | Market Size, Segments Analysis, Competitive Landscape, Regional Analysis, DROC & SWOT Analysis, Forecast Outlook |
| Key Segments | • By Component (Solutions and Services) • By Device Type (Hospital Medical Devices, Internally Embedded Medical Devices, and Wearable and External Medical Devices) • By Deployment Mode (On-Premises and Cloud-Based) • By End User (Healthcare Providers, Medical Device Manufacturers, and Healthcare Payers) |
| Regional Analysis/Coverage | North America (US, Canada), Europe (Germany, UK, France, Italy, Spain, Russia, Poland, Rest of Europe), Asia Pacific (China, India, Japan, South Korea, Australia, ASEAN Countries, Rest of Asia Pacific), Middle East & Africa (UAE, Saudi Arabia, Qatar, South Africa, Rest of Middle East & Africa), Latin America (Brazil, Argentina, Mexico, Colombia, Rest of Latin America). |
| Company Profiles | Palo Alto Networks, Inc., Cisco Systems, Inc., Check Point Software Technologies Ltd., Armis, Inc., Claroty Ltd., Forescout Technologies, Inc., Axonius, Inc. (Cynerio), Ordr, Inc., Medcrypt, Inc., Synopsys, Inc., ClearDATA, GE HealthCare, Fortinet, Inc., Zscaler, Inc. |

Frequently Asked Questions
The market was valued at USD 10.15 Billion in 2025 and is expected to reach USD 11.15 Billion in 2026 and USD 26.02 Billion by 2035.
The market is projected to grow at a CAGR of 9.87% from 2026 to 2035.
North America leads with a 41.86% share in 2025, supported by premarket cybersecurity requirements and a large connected device base.
Asia Pacific is expected to grow fastest, at a CAGR of 10.89% from 2026 to 2035.
Solutions, hospital medical devices, on-premises deployments, and healthcare providers lead their respective segments. Services, wearable and external medical devices, cloud-based deployments, and medical device manufacturers are the fastest growing.
Palo Alto Networks, Inc., Cisco Systems, Inc., Check Point Software Technologies Ltd., Armis, Inc., and Claroty Ltd. are among the major players.
Legacy devices, skills shortages, operational risk from scanning and blocking, and fragmented budgets are the main challenges.
